Only logged in customers who have purchased this product may leave a review.
Preview
Availability: Available immediately
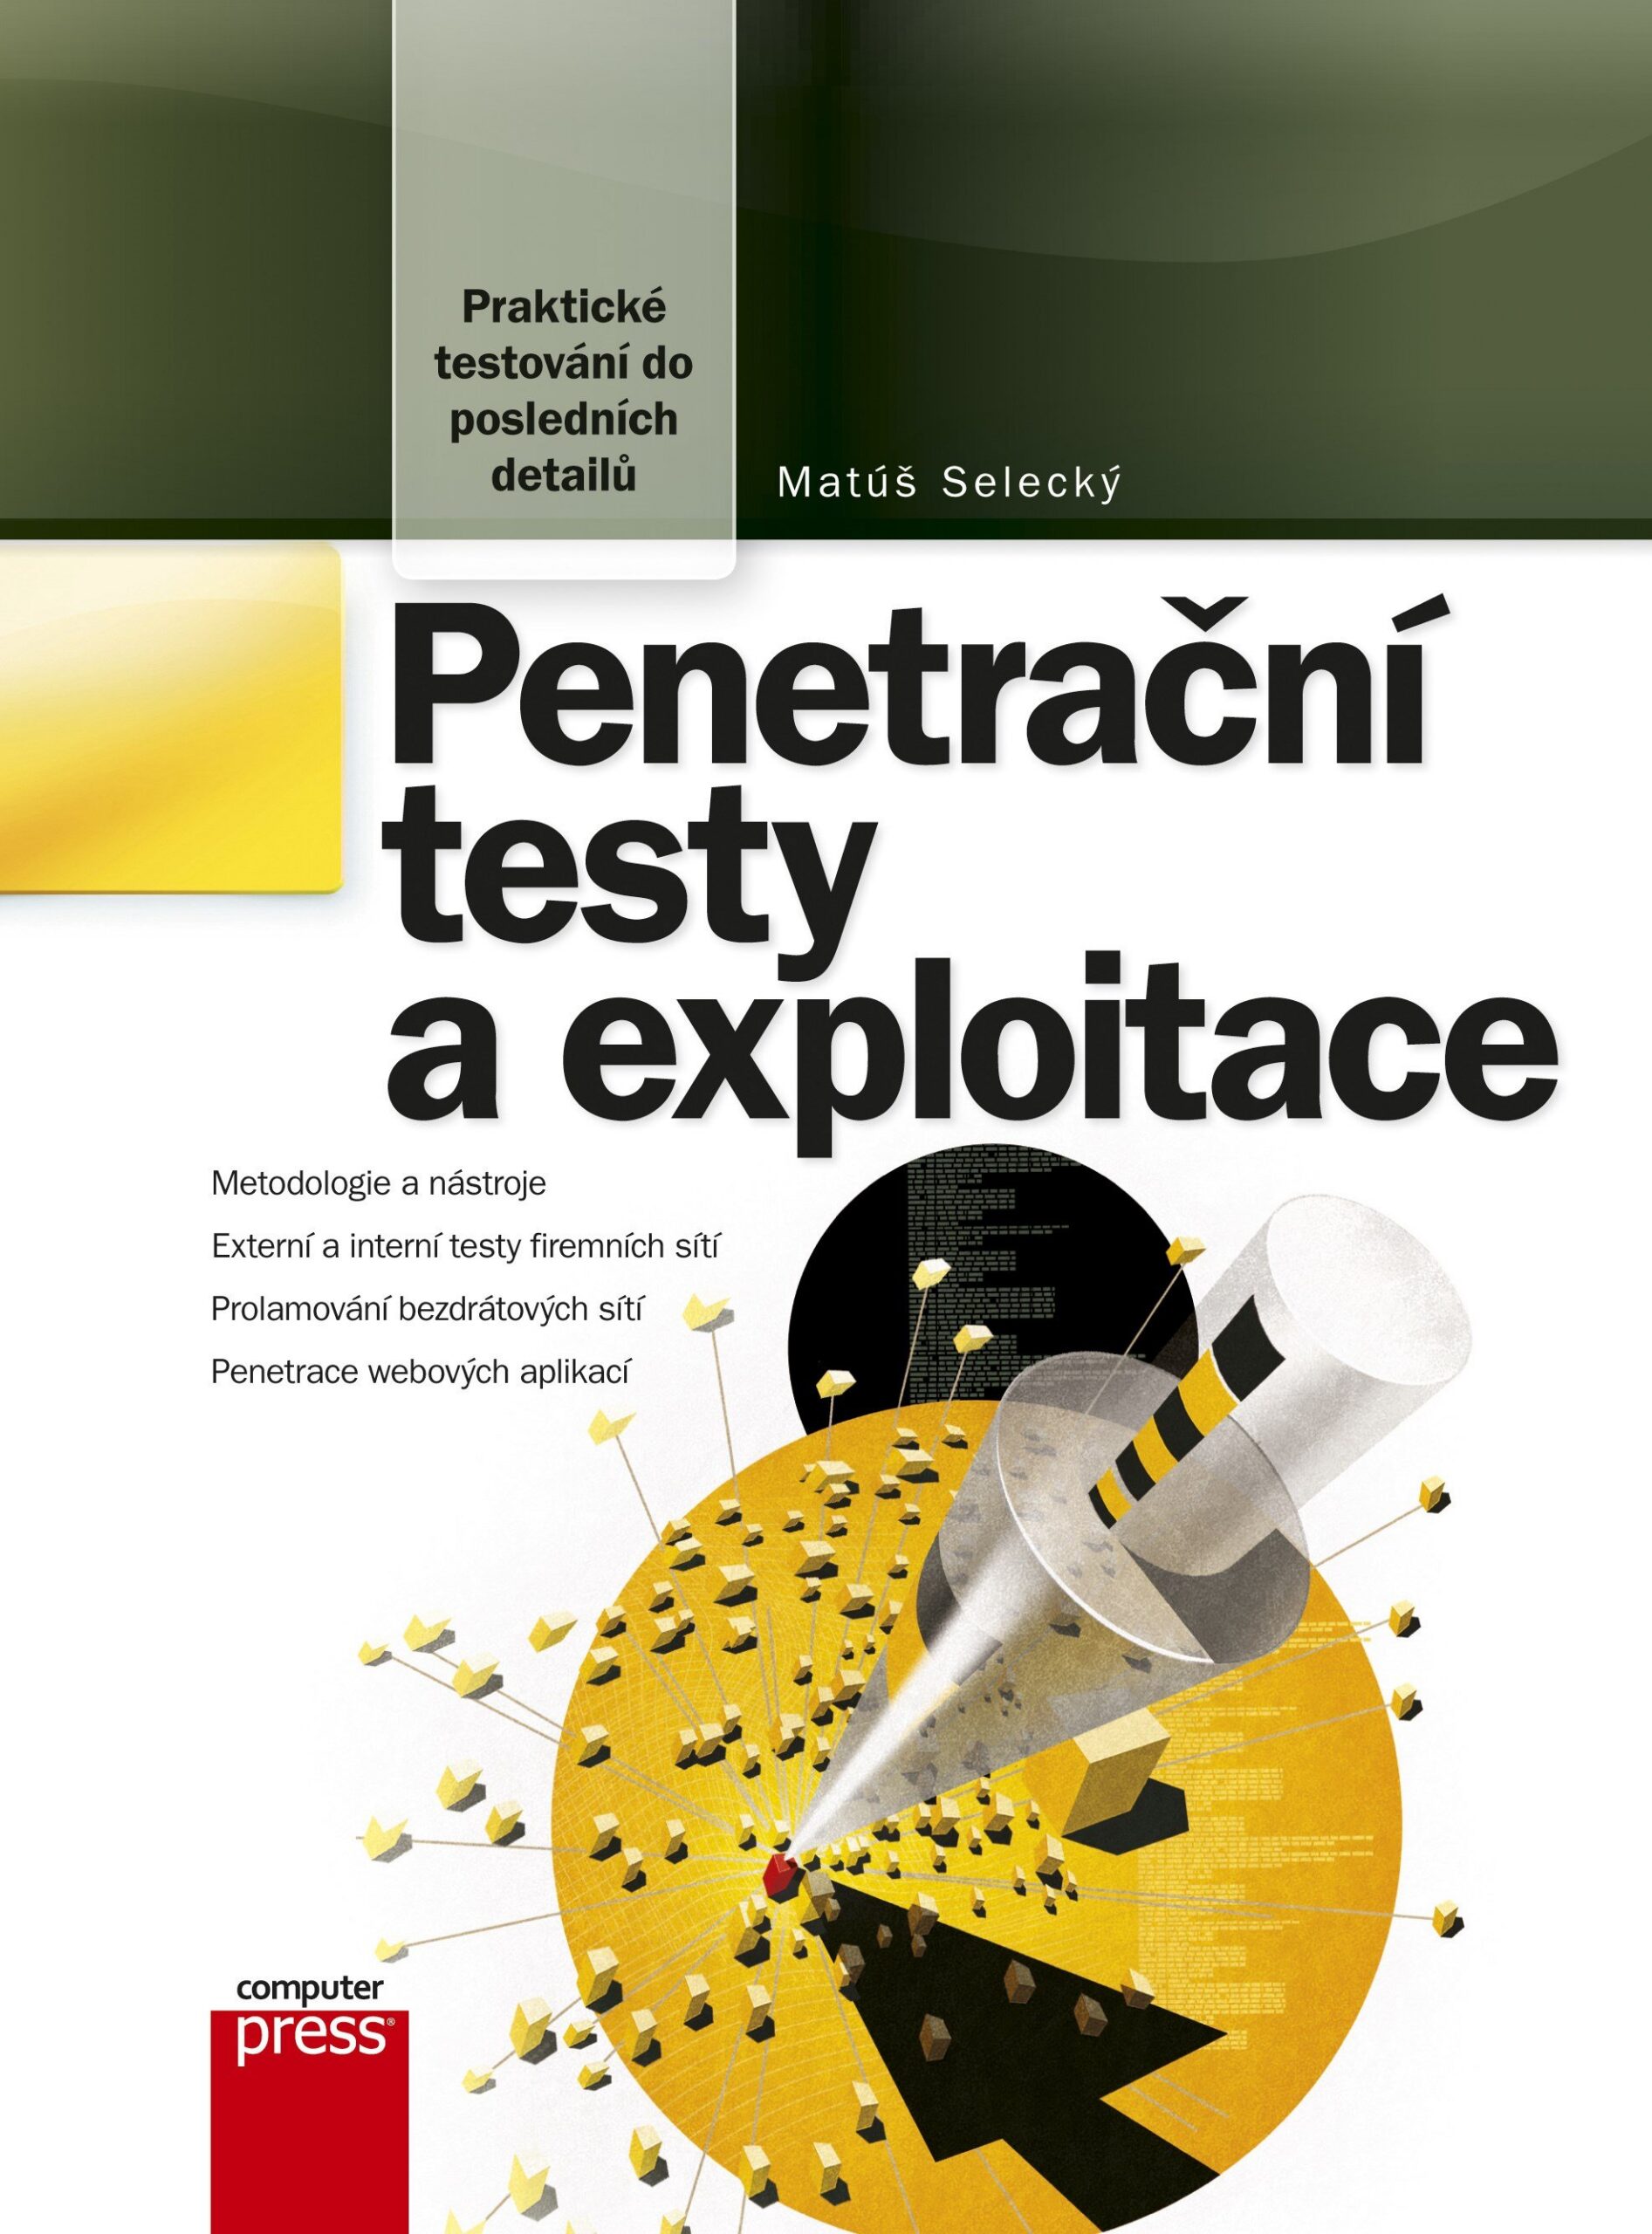
Penetrační testy a exploitace
Author: Matúš Selecký
15,56 €
Penetrační testy a exploitace presents security testing as an organized process rather than simply a collection of tools. Matúš Selecký connects methodology with examples of applications used to examine different parts of an IT environment. The book distinguishes external and internal perspectives on a corporate network and covers wireless networks and web applications. It is intended for readers who need to understand the structure of a test and how its results are recorded. Its subject matter is specialist and practically oriented.
A shared chapter structure shows how general methodology applies to different areas of security. Readers encounter a tool, its basic use, and a sample test with output. This format helps connect a specific result with the question the assessment was meant to answer.
The publication covers external and internal corporate-network testing, wireless environments, and web applications. These areas differ in what they examine, but share a need for systematic procedures and an understanding of findings. References to further information offer scope for independent study.
Choosing the book also depends on whether the reader wants a methodological overview or study of a specific area. The range of environments makes it possible to compare different test types. Applications and their versions belong to the technical context of this edition.
Penetrační testy a exploitace presents security testing as an organized process rather than simply a collection of tools. Matúš Selecký connects methodology with examples of applications used to examine different parts of an IT environment. The book distinguishes external and internal perspectives on a corporate network and covers wireless networks and web applications. It is intended for readers who need to understand the structure of a test and how its results are recorded. Its subject matter is specialist and practically oriented.
Book information
- Author
- Matúš Selecký
- Publisher
- Albatros Media a.s.
- Imprint
- Computer Press
- Formát
- E-book
- Language
- Czech
- Genre
- informační bezpečnost, penetrační testování, počítačové sítě, webová bezpečnost
- ISBN
- 978-80-251-3752-9
- Pages
- 304
- E-book formats
- EPUB (ISBN 978-80-251-3893-9) · PDF (ISBN 978-80-251-3892-2) · MOBI (ISBN 978-80-251-3894-6)
What is Penetrační testy a exploitace about?
A shared chapter structure shows how general methodology applies to different areas of security. Readers encounter a tool, its basic use, and a sample test with output. This format helps connect a specific result with the question the assessment was meant to answer.
The publication covers external and internal corporate-network testing, wireless environments, and web applications. These areas differ in what they examine, but share a need for systematic procedures and an understanding of findings. References to further information offer scope for independent study.
Choosing the book also depends on whether the reader wants a methodological overview or study of a specific area. The range of environments makes it possible to compare different test types. Applications and their versions belong to the technical context of this edition.
Themes and motifs
Testing methodology
A consistent structure connects the task, tool, and interpretation of output.
Different environments
Network, wireless, and web security require different perspectives.
Practical examples
Output listings and annotated tests complement the overview of tools.
Who is this book for?
For network administrators, security students, and professionals engaged in specialist IT security assessment.
Book context
This Czech technical guide by Slovak author Matúš Selecký was published by Computer Press. SOURCE_FACT lists 304 pages and ISBN 978-80-251-3752-9. The official Albatros Media record confirms 304 pages and September 17, 2012, as the publication date. Library catalogs list the first edition in Brno in 2012 with 303 numbered pages, a common difference between a bibliographic physical description and the commercial figure of 304 pages. SOURCE_FACT has no date, and its 304-page figure remains authoritative for this edition.
Otázky o knihe
What is Penetrační testy a exploitace about?
Penetrační testy a exploitace presents security testing as an organized process rather than simply a collection of tools.
What language is this edition in?
This edition is in Czech.
Which ebook formats are available?
EPUB, PDF, MOBI.
Which testing areas does the book cover?
External and internal corporate-network tests, wireless networks, and web applications, covering both methodology and tools.

Reviews
There are no reviews yet.